Zookeeper's ACL (Access Control List) permissions are especially important in production environments, so this chapter provides a special introduction.
ACL permissions can set related read/write permissions for nodes to ensure data security.
permissions can specify different permission scopes and roles.
ACL Command Line
- getAcl command: Get the ACL permission information of a node.
- setAcl command: Set the ACL permission information of a node.
- addauth command: Enter authentication and authorization information. Enter the plaintext password during registration, and it is saved in encrypted form.
ACL Composition
Zookeeper's ACL consists of[scheme:id:permissions]to form the permission list.
- 1、scheme: Represents the permission mechanism adopted, including world, auth, digest, ip, super.
- 2、id: Represents the users allowed to access.
- 3、permissions: Permission combination string, composed of cdrwa, where each letter represents a different permission: create permission (c), delete permission (d), read permission (r), write permission (w), admin permission (a).
world Example
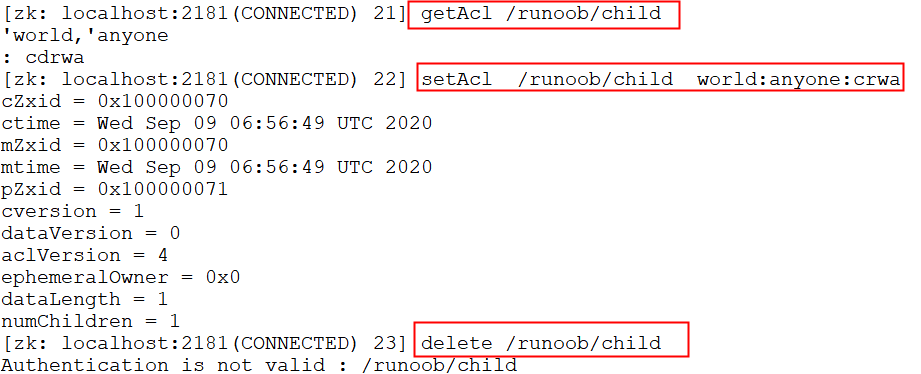
Check the default node permissions, then update the node's permissions section to crwa. As a result, deleting the node fails. Here, world represents open permissions.
$ getAcl /example/child
$ setAcl /example/child world:anyone:crwa
$ delete /example/child
auth Example
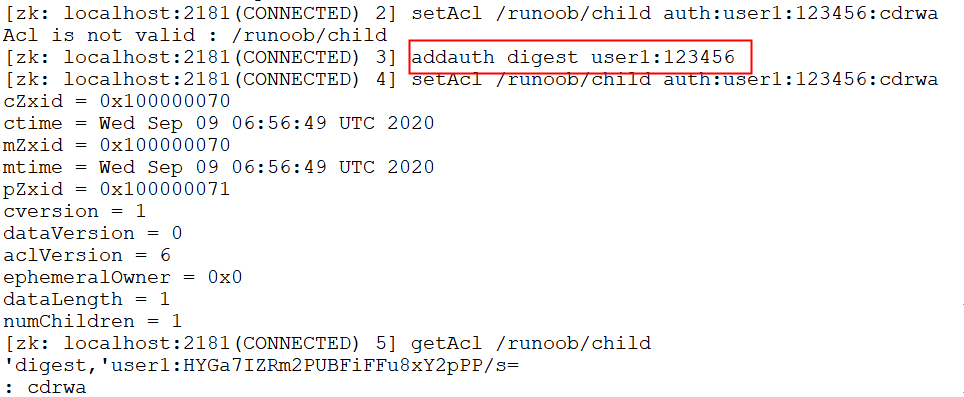
auth is used to grant permissions. Note that you need to create a user first.
$ setAcl /example/child auth:user1:123456:cdrwa
$ addauth digest user1:123456
$ setAcl /example/child auth:user1:123456:cdrwa
$ getAcl /example/child
digest Example
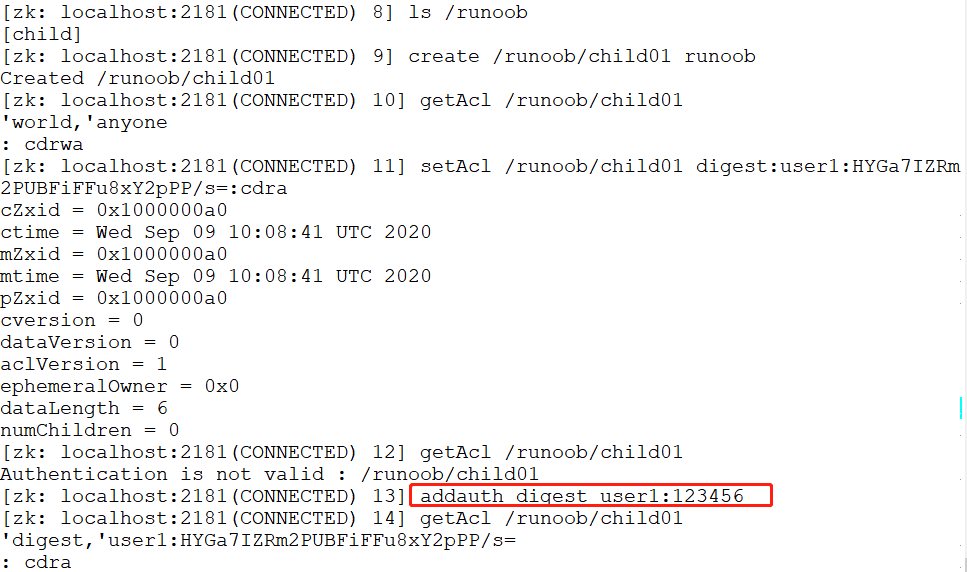
Log out of the current user, reconnect to the terminal. digest can be used for account/password login and verification.
$ ls /example
$ create /example/child01 example
$ getAcl /example/child01
$ setAcl /example/child01 digest:user1:HYGa7IZRm2PUBFiFFu8xY2pPP/s=:cdra
$ getAcl /example/child01
$ addauth digest user1:123456
$ getAcl /example/child01
Note:The encrypted password is the one created in the previous step.
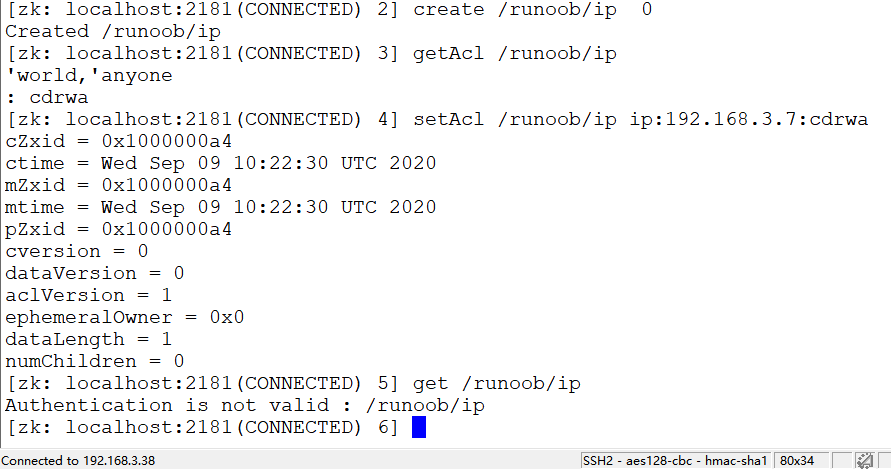
IP Example
Restrict IP address access permissions. After setting permissions to IP address 192.168.3.7, the IP 192.168.3.38 no longer has access permissions.
$ create /example/ip 0
$ getAcl /example/ip
$ setAcl /example/ip ip:192.168.3.7:cdrwa
$ get /example/ip